


Network-Security-Essentials Exam Info and Free Practice Test All-in-One Exam Guide Apr-2025
Pass WatchGuard Network-Security-Essentials Actual Free Exam Q&As Updated Dump Apr 26, 2025
NEW QUESTION # 15
What steps must you take to send log messages from a Firebox to WatchGuard Cloud? (Select two.)
- A. Add the FQDN of your WatchGuard Cloud account as a Log Server on the Firebox
- B. Define an Authentication Key that all your Fireboxes use to communicate with WatchGuard Cloud
- C. Configure Dimension to synchronize log messages with WatchGuard Cloud
- D. Enable WatchGuard Cloud in the Firebox configuration
- E. Use the WatchGuard Cloud Add Device wizard to add the Firebox to WatchGuard Cloud
Answer: D,E
Explanation:
* Enable WatchGuard Cloud in Firebox Configuration: To send log messages to WatchGuard Cloud, you need to activate WatchGuard Cloud integration within the Firebox's configuration settings. This action prepares the device to communicate with WatchGuard Cloud and transfer log data.
* Use the WatchGuard Cloud Add Device Wizard: The Add Device wizard in WatchGuard Cloud is used to register and connect the Firebox to WatchGuard Cloud. This wizard guides administrators through the setup and ensures that the device is correctly configured to send logs and other data to the cloud.
These steps are required to establish connectivity and ensure that log messages are sent to WatchGuard Cloud.
Other options, such as adding an FQDN or configuring Dimension synchronization, are not necessary for this task.
NEW QUESTION # 16
You can run TCP Dump directly from the Firebox.
- A. False
- B. True
Answer: A
Explanation:
You cannot runTCP Dumpdirectly from a Firebox device. While Firebox has various monitoring tools such as Traffic Monitor and Firebox System Manager, it does not natively support TCP Dump, which is a command-line tool primarily available on Linux-based systems. Instead, packet captures and traffic monitoring need to be handled through Firebox-specific tools or by exporting logs to external devices for further analysis.
NEW QUESTION # 17
Users cannot download a PDF file from your intranet. You know the file is safe to download. When you review the log messages, you see that IntelligentAV identified the file as malicious. The only way to resolve this is to change the file extension.
- A. False
- B. True
Answer: A
Explanation:
When IntelligentAV identifies a file as malicious, users have options other than changing the file extension to resolve the issue. IntelligentAV relies on AI-driven detection, and if the PDF file isknown to be safe, an administrator can manually adjust the IntelligentAV settings or add an exception for the specific file.
Changing the file extension alone does not address the root of the detection and is not a reliable solution to bypass IntelligentAV checks.
NEW QUESTION # 18
If a Firebox has two trusted interfaces enabled, the default policies allow HTTPS connections between computers on different trusted networks.
- A. False
- B. True
Answer: A
Explanation:
By default, Firebox policies do not allow HTTPS connections between devices on separate trusted networks without specific policy configuration. Firebox's default security posture is to restrict inter-network traffic unless explicitly permitted, enhancing network segmentation and security within trusted zones.
NEW QUESTION # 19
With the policies configured as shown in this image, HTTP traffic can be sent and received through Branch Office VPN tunnel 1 and tunnel 2.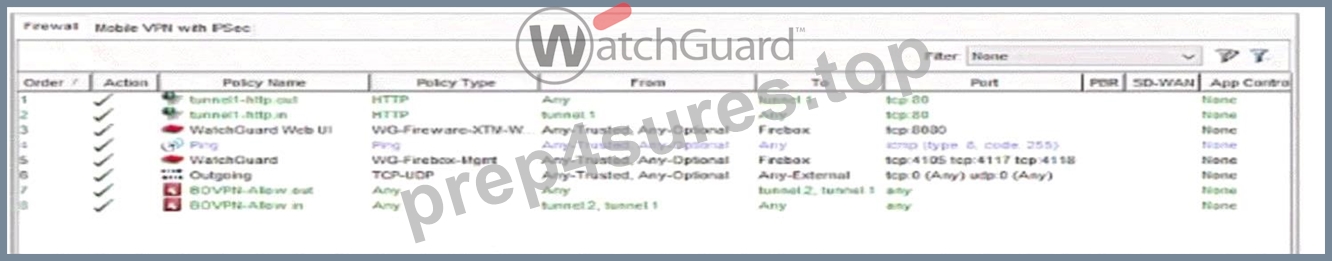
- A. False
- B. True
Answer: B
Explanation:
The image shows firewall policies allowing HTTP traffic throughBranch Office VPN (BOVPN)tunnel 1 and tunnel 2:
* tunnel1-http.outpolicy: Allows HTTP traffic (TCP port 80) fromAnysource totunnel 1.
* tunnel1-http.inpolicy: Allows HTTP traffic fromtunnel 1toAnydestination.
* BOVPN-Allow.outandBOVPN-Allow.inpolicies: Configured to allowAnytraffic betweentunnel 2and tunnel 1in both directions.
These configurations indicate that HTTP traffic is permitted through both tunnels, enabling it to be sent and received across BOVPN tunnels 1 and 2. Thus, users on either end of these VPN tunnels can transmit HTTP traffic successfully.
NEW QUESTION # 20
If policies are automatically ordered, which of these policies has the highest precedence? (Select one.)
- A. HTTPS policy - From: User1@Firebox-DB To: Any-External
- B. HTTPS policy - From: Any-Trusted, Any-Optional To: Any-External
- C. Outgoing policy - From: Any-Trusted, Any-Optional To: Any-External
- D. HTTPS policy - From: Trusted To: Any-External
Answer: A
Explanation:
When policies are automatically ordered, policies with more specific user-based criteria have higher precedence over general policies. In this scenario, an HTTPS policy for a specific user (e.g.,User1@Firebox- DB) would take precedence over policies that apply to broader groups or networks, such asAny-Trustedor Any-Optional. This ordering ensures that individual user rules are evaluated first before generic policies, providing finer access control.
NEW QUESTION # 21
After you enable content inspection, your users see a certificate warning when they browse the Internet. What is one way to resolve this? (Select one.)
- A. Configure the HTTPS proxy policy to allow inbound traffic from your CA
- B. Import a trusted web server certificate to the Firebox
- C. Install the current Firebox Proxy Authority certificate on your user workstations
- D. Configure a WebBlocker exception for your certificate server
Answer: C
Explanation:
When content inspection is enabled on a Firebox, it decrypts HTTPS traffic for inspection, which requires presenting its own certificate to the client devices. This often causes certificate warnings in web browsers because the certificate issued by the Firebox is not inherently trusted by the client browsers. To resolve this, you need to install the Firebox'sProxy Authority certificateon each user's workstation as a trusted certificate. This action will prevent browsers from displaying certificate warnings, as they will recognize the Firebox certificate as a trusted source for secure connections.
NEW QUESTION # 22
If you have only one public IP address, can you use Static NAT to enable inbound connections to both an email server and a web server on the private network? (Select one.)
- A. No, you must use Dynamic NAT to route inbound connections to more than one server
- B. No, you must assign a public IP address to each server
- C. Yes, if both servers use different ports
- D. Yes, if both servers are on different private subnets
Answer: C
Explanation:
With only one public IP address, you can still configure Static NAT to route connections to both an email server and a web server, as long as each service is accessed on a different port. For instance, HTTP/HTTPS traffic for the web server can use port 80/443, while the email server can use ports associated with email protocols (e.g., 25 for SMTP). Static NAT can direct incoming requests to different internal servers based on port, making this approach feasible.
NEW QUESTION # 23
You have five public IP addresses available from your ISP. When you create a Static NAT action, you want to specify one of the public IP addresses for inbound traffic but do not see it in the IP address drop-down list.
How can you change the Firebox configuration to see additional public IP addresses in the Static NAT action?
(Select one.)
- A. Add secondary IP addresses to the external interface
- B. Configure 1-to-1 NAT for your entire subnet
- C. Enable the Set Source IP option in the policy
- D. Add the IP addresses to the Dynamic NAT configuration
- E. Add the public IP addresses to the From field of the policy that uses the Static NAT action
Answer: A
Explanation:
To use additional public IP addresses in a Static NAT action, you need to add them as secondary IP addresses to the external interface on the Firebox. By adding these IPs as secondary addresses, they become selectable options in the Static NAT configuration, allowing inbound traffic to be routed based on specific public IPs allocated by the ISP.
NEW QUESTION # 24
When does a network host make an ARP request? (Select one.)
- A. To find the IP address of the default gateway
- B. To find the IP address associated with a MAC address
- C. To find the IP address associated with a hostname
- D. To find the hostname associated with an IP address
- E. To find the MAC address associated with an IP address
Answer: E
Explanation:
The Address Resolution Protocol (ARP) is used to map an IP address to a physical machine (MAC) address on a local network. When a device wants to communicate with another device on the same local network, it uses an ARP request to discover the MAC address associated with a known IP address. The ARP process is essential for IP-based communication within the same network segment.
* Option Dis correct because ARP's primary function is to find the MAC address associated with an IP address.
* Other options mention IP addresses or hostnames, which would be resolved using other methods like DNS, not ARP.
NEW QUESTION # 25
Which of these options are private IPv4 address spaces described in RFC 1918 Address Allocation for Private Internets? (Select three.)
- A. 192.168.0.0/16
- B. 10.0.0.0/8
- C. 172.0.0.0/16
- D. 102.0.2.0/24
- E. 172.16.0.0/12
Answer: A,B,E
Explanation:
RFC 1918 defines private IP address spaces that are not routable on the public internet and are reserved for internal network use:
* 10.0.0.0/8: Covers IP addresses from 10.0.0.0 to 10.255.255.255 and is often used in large private networks.
* 172.16.0.0/12: Covers addresses from 172.16.0.0 to 172.31.255.255 and is commonly used in medium- sized networks.
* 192.168.0.0/16: Covers addresses from 192.168.0.0 to 192.168.255.255 and is frequently used in small to medium networks, especially for home and office routers.
* Option C(102.0.2.0/24) andOption D(172.0.0.0/16) are not private address spaces according to RFC
1918.
NEW QUESTION # 26
There is an Internet outage at your primary ISP, but the Internet connection from the Firebox has not failed over to your backup ISP. Both ISP connectors are correctly cabled and have active physical links. What could cause this problem? (Select two.)
- A. In the Multi-WAN settings, the Gradual Fallback option is enabled
- B. The secondary IP addresses are not defined for the backup ISP interface
- C. In the Multi-WAN settings, the Immediate Fallback option is enabled
- D. Link Monitor target for the backup ISP interface is not responding
- E. The Link Monitor target for the primary ISP interface is set to ping the default gateway, but the outage is further upstream
Answer: D,E
Explanation:
* Link Monitor Target for Backup ISP: If the backup ISP's Link Monitor target is not responsive, the Firebox will not initiate a failover, as it interprets the backup connection as inactive or faulty.
* Primary ISP Link Monitor Configuration: When the Link Monitor for the primary ISP only checks the default gateway, it may not detect issues occurring further upstream. If the outage is beyond the gateway, failover will not activate because the monitor assumes the link is still valid.
These settings are critical to ensuring proper Multi-WAN failover behavior in case of ISP issues.
NEW QUESTION # 27
You lost access to a Firebox because no one knows the administrator passphrase. How can you regain access to the Firebox? (Select one.)
- A. Plug in a USB flash drive with the WatchGuard Password Reset utility loaded
- B. Restore a backup image of the Firebox
- C. Connect with a console cable to reset the passphrase
- D. Call WatchGuard Support for a passphrase reset
- E. Reset the Firebox to its factory defaults
Answer: E
Explanation:
If the administrator passphrase is lost:
* Option A: Resetting the Firebox to factory defaults is the recommended solution to regain access, as it clears the current configurations, including the admin passphrase, allowing reconfiguration from scratch.
* Option B(USB reset utility) andOption E(console cable reset) are not standard options for passphrase recovery on Firebox.
* Option C(Calling WatchGuard Support) cannot directly reset the passphrase.
* Option D(Restoring a backup) requires access to the device with the current passphrase.
NEW QUESTION # 28
A Firebox has an external IP address of 203.0.113.100. A public web server with the IP address 10.0.1.80 is connected to a Firebox internal network. What is the effect of the policy shown in this image? (Select one.)
- A. Allows users on the Internet and the 10.0.1.0/24 network to use the internal IP address of the Firebox to connect to the web server
- B. Allows users on the Internet to connect to the 10.0.1.80 IP address of the web server
- C. Applies dynamic NAT to the 10.0.1.80 IP address of the web server to allow inbound connections
- D. Allows users on the Internet and the 10.0.1.0/24 network to use the external IP address of the Firebox to connect to the web server
Answer: D
Explanation:
In the policy configuration shown in the image:
* From Section: It specifies "Any-External" and 10.0.1.0/24, indicating that this policy applies to traffic from any external source (Internet users) as well as from devices on the internal network 10.0.1.0/24.
* To Section: The destination specifies a public-facing IP address (203.0.113.100) that is statically NAT'd to the internal IP address of the web server (10.0.1.80). This means external users and internal users can access the web server using the Firebox's external IP.
* Effect of Static NAT: The policy uses Static NAT to map the Firebox's external IP address to the web server's internal IP address, allowing inbound connections to reach the server. This setup provides consistent access for both external and internal users via the same public IP address.
This configuration effectively enables both Internet users and users within the specified internal network (10.0.1.0/24) to connect to the web server using the Firebox's external IP, makingOption Dthe correct answer.
NEW QUESTION # 29
Which of these is a network IP address? (Select one.)
- A. 10 10 10 255/24
- B. 10 0.1 255 8
- C. 172 16 100 1/12
- D. 1G2 153 10 O 1
- E. 1Q2 158.10 0-24
Answer: A
Explanation:
In this question, we need to identify the correctly formatted network IP address. IPv4 addresses are represented in a dotted decimal format, typically in the form of x.x.x.x/n, where x represents decimal values from 0 to 255, and /n is the CIDR notation indicating the subnet mask. Among the options:
* Option E (10 10 10 255/24)fits the IPv4 standard and CIDR notation.
* The other options contain invalid characters or formats (letters like "G" or "Q" or unusual symbols like
"O" or "-") and do not conform to IP addressing standards.
NEW QUESTION # 30
What type of NAT enables clients on a private network to connect to servers on the Internet? (Select one.)
- A. Hairpin NAT
- B. NAT loopback
- C. Dynamic NAT
- D. Static NAT
Answer: C
Explanation:
Dynamic NAT enables clients on a private network to connect to servers on the Internet. By translating private IP addresses to a public IP address (or pool of addresses), Dynamic NAT allows multiple devices within a private network to access external resources on the Internet. This form of NAT is essential in conserving IP addresses and maintaining privacy for internal network topologies.
NEW QUESTION # 31
Some management tasks require you to use a specific management interface. Match the task below with the management interface that supports it.
Answer:
Explanation:
Explanation:
Here are the correct answers based on typical Firebox management interface capabilities:
* Edit a configuration file without being connected to a Fireboxanswer: Policy Manager Policy Manager allows administrators to edit a Firebox configuration file offline without a direct connection to the Firebox. This feature is helpful for preparing configuration changes in advance.
* Run Policy Checkeranswer: Policy Manager
The Policy Checker tool is included in Policy Manager, which checks configuration settings for errors before applying them. This tool provides an essential layer of validation, preventing misconfigurations.
* View the Firebox Status Reportanswer: Firebox System Manager
The Firebox System Manager (FSM) interface provides real-time status reporting on device health, traffic, and security services, which includes viewing the Firebox Status Report.
* Schedule a Firebox OS updateanswer: Fireware Web UI
Fireware Web UI includes options for scheduling OS updates for the Firebox, which can be managed remotely through a web interface.
These answers align with standard Firebox network security essentials and their recommended management interfaces for specific administrative tasks. Let me know if you need further assistance with related Firebox management topics
NEW QUESTION # 32
In Firebox System Manager, where can you perform each of these tasks?
Answer:
Explanation:
Explanation:
Here are the correct answers based on the Firebox System Manager interface functions:
* See the routing table and interface statisticsanswer:Firebox System Manager - Status Report Explanation: The Status Report section in Firebox System Manager includes information on network routing and interface statistics, providing insights into network paths and interface performance.
* See a list of users connected to the Fireboxanswer:Firebox System Manager - Authentication List Explanation: The Authentication List displays all active user sessions connected to the Firebox, showing authenticated users and their session details.
* Learn the status of your IPS signature databaseanswer:Firebox System Manager - Subscription Services Explanation: Subscription Services in FSM gives information on the status of services like IPS, showing the update status and version of the signature database.
* Ping the source of a denied packetanswer:Firebox System Manager - Traffic Monitor Explanation: The Traffic Monitor tool allows administrators to track packet details and offers functionality to ping sources directly, aiding in network troubleshooting.
* Block all traffic for an IP addressanswer:Firebox System Manager - Blocked Sites List Explanation: The Blocked Sites List feature in FSM lets administrators add IP addresses to a blacklist, blocking all incoming and outgoing traffic for specified addresses.
These answers utilize standard Firebox management features for performing administrative and diagnostic tasks efficiently. Let me know if you need further assistance with Firebox System Manager capabilities.
NEW QUESTION # 33
You recently installed network monitoring software on your server and then performed a port scan for each IP address in the network. When the scan finishes, you notice that the server lost access to the Internet. What is the most likely cause of this issue? (Select one.)
- A. The server IP address was added to the Blocked Sites list because an IPS signature was matchedduring the port scan
- B. The server IP address was added to the Blocked Sites list because the network was flooded with ESP traffic during the port scan
- C. The policy that handles outbound traffic was automatically disabled because the Firebox was port scanned
- D. The server IP address was added to the Blocked Sites list because of the default packet handling port scan rule
- E. The port scan traffic matched a default HTTP proxy content type rule configured with a Block action
Answer: D
Explanation:
When a port scan is detected, Firebox devices with default settings often include a rule to add the source IP address of the scan to the Blocked Sites list to prevent potential threats. This is a standard security measure in Firebox configurations, aimed at mitigating the risk of network scanning attempts. Consequently, if the server you used to perform the port scan was added to the Blocked Sites list, it would lose Internet access as the device blocks any outgoing connections from that IP. This behavior aligns with Firebox's handling of port scan detection through default security rules.
NEW QUESTION # 34
When you configure a Branch Office VPN tunnel to a third-party device, AES-GCM encryption is recommended for:
- A. Connections to third-party firewalls only
- B. Better performance and throughput when supported by both VPN endpoints
- C. Better uptime because of additional keep-alive options
- D. Routing over a BOVPN
- E. Troubleshooting purposes
Answer: B
Explanation:
AES-GCM (Galois/Counter Mode)encryption is recommended for VPNs because it provides strong encryption with high performance and low overhead, making it an ideal choice for environments where both endpoints support it. AES-GCM combines encryption and authentication in a single step, resulting in faster processing compared to traditional encryption modes that handle these tasks separately. This mode is advantageous for maintaining high throughput in VPN tunnels, especially beneficial for branch office or inter- site VPNs where performance is critical.
NEW QUESTION # 35
You have an existing network infrastructure built out that uses tagged and untagged VLAN networks. Based on the diagram below, which VLANs must you add to the Firebox interface? (Select one.)
- A. VLAN 10 Tagged and VLAN 20 Untagged
- B. VLAN 10 Tagged and VLAN 20 Tagged
- C. VLAN 10 Untagged and VLAN 20 Untagged
- D. VLAN 10 Untagged, VLAN 10 Tagged, and VLAN 20 Tagged
- E. VLAN 10 Untagged and VLAN 20 Tagged
Answer: B
Explanation:
Based on the diagram provided, the Firebox connects to a switch with VLAN 10 and VLAN 20 as tagged traffic. The connection between the Firebox and the switch shows that both VLAN 10 and VLAN 20 are tagged, indicating that traffic for these VLANs will be carried over a single trunk link to the Firebox.
To properly configure the Firebox to handle this setup, you need to addVLAN 10 TaggedandVLAN 20 Taggedto the Firebox interface, as this configuration will allow the Firebox to interpret tagged packets for both VLANs from the switch. Untagged configurations are not applicable here since the Firebox interface expects tagged traffic for both VLANs on the trunk connection.
NEW QUESTION # 36
Clients on the 10.0.10.0/24 network must connect to the server at 10.0.20.100. Based on this image, what static route must you add to the Firebox for traffic to reach the server? (Select one.)
- A. Route to 10.0.20.0/24, Gateway 10.0.2.254
- B. Route to 10.0.20.0/24, Gateway 10.0.2.1
- C. Route to 10.0.2.0/24, Gateway 10.0.2.1
- D. Route to 10.0.10.0/24, Gateway 10.0.0.1
- E. Route to 10.0.20.0/24, Gateway 10.0.2.254
Answer: A
Explanation:
In this network configuration:
* The Firebox needs a static route to direct traffic intended for the 10.0.20.0/24 network (where the server
10.0.20.100 resides).
* The gateway address that allows the Firebox to reach the 10.0.20.0/24 network is 10.0.2.254, which is the router's IP address on the 10.0.2.0/24 network.
By configuring a static route:
* Destination: 10.0.20.0/24
* Gateway: 10.0.2.254
This route instructs the Firebox to send traffic destined for the 10.0.20.0/24 network via the router at
10.0.2.254, enabling clients in the 10.0.10.0/24 network to reach the server.
* Option Bis correct because it provides the correct destination and gateway for traffic to the 10.0.20.0
/24 network.
* Option Aincorrectly sets the route to 10.0.10.0/24, which doesn't address the server network.
* Options C and Dset incorrect gateways (10.0.2.1), which do not route traffic correctly in this setup.
* Option Eis a duplicate of B and would also be correct; thus, B and E are equivalent.
NEW QUESTION # 37
You want to create a branch office VPN virtual interface between a remote Firebox and your headquarters Firebox so the remote Firebox can send log data to a server at headquarters. For the log data to be sent from the remote Firebox over the VPN successfully, what BOVPN virtual interface setting must you configure?
(Select one.)
- A. Virtual IP addresses
- B. An IPSec certificate, instead of a Pre-shared key
- C. Dead Peer Detection (DPD)
- D. Perfect Forward Secrecy (PFS)
- E. IKEv2 in the Phase 1 settings
Answer: A
Explanation:
To enable the remote Firebox to send log data to a server at headquarters through a Branch Office VPN (BOVPN) virtual interface, you must configureVirtual IP addresses. Virtual IPs enable devices on either end of the VPN tunnel to communicate as if they are on the same network, facilitating routing of log data from the remote Firebox to the log server located at headquarters.
Other options likeIPSec certificatesandIKEv2are not specifically required for this configuration, though they can enhance security.Dead Peer Detection (DPD)andPerfect Forward Secrecy (PFS)are useful for maintaining VPN stability and security but are not directly necessary for enabling log transmission.
NEW QUESTION # 38
Before packets are examined by Default Threat Protection, they are processed by firewall policies in top- down order.
- A. False
- B. True
Answer: B
Explanation:
In Firebox configuration, packets are processed by firewall policies in atop-down orderbefore they reach Default Threat Protection. This ordering ensures that the firewall policies defined higher in the policy list take precedence. Packets are evaluated against each rule sequentially from top to bottom until a matching policy is found, which then determines the action taken (allow, deny, or inspect further). Only after this process will any unfiltered traffic be subject to Default Threat Protection for additional security checks.
NEW QUESTION # 39
......
Online Questions - Valid Practice Network-Security-Essentials Exam Dumps Test Questions: https://www.prep4sures.top/Network-Security-Essentials-exam-dumps-torrent.html
Latest Network-Security-Essentials Actual Free Exam Updated 60 Questions: https://drive.google.com/open?id=1OOV1u8p585zZNPuCgWXJjjOfUNPG3hpX