


[Sep-2026] IdentityIQ-Engineer Dumps PDF - IdentityIQ-Engineer Real Exam Questions Answers
IdentityIQ-Engineer Dumps 100% Pass Guarantee With Latest Demo
NEW QUESTION # 62
Can the following IdentitylQ object be extended to store client-specific data by updating the corresponding .HBM file?
Solution: Link
- A. Yes
- B. No
Answer: B
Explanation:
In SailPoint IdentityIQ, certain objects, such as the Link object, cannot be directly extended by updating the corresponding .HBM (Hibernate Mapping) file. Modifying or extending core IdentityIQ objects typically requires a deeper level of customization involving the extension of the application schema and possibly custom Java code. The .HBM files are part of IdentityIQ's internal persistence framework, and altering them is not a supported or recommended method for extending objects in a production environment. Customization should instead be done using SailPoint's supported extension points, such as using ManagedAttributes or CustomAttributes within the IdentityIQ application framework. For guidelines on extending IdentityIQ objects, refer to the SailPoint IdentityIQ Customization Guide and best practices documentation.
Top of Form
Bottom of Form
NEW QUESTION # 63
Is the following statement about workflows and sub-workflows (subprocesses) true?
Proposed Solution:
Many standard LCM sub-workflows can be leveraged in custom workflows, with their behavior controlled via input variables.
- A. Yes
- B. No
Answer: A
Explanation:
Yes. IdentityIQ's Lifecycle Manager workflows are built from reusable workflow components and subprocesses. Many standard LCM subprocesses can be called from custom workflows, provided the engineer understands the expected input variables, return variables, and control flags. This is a preferred engineering pattern because it avoids rewriting complex provisioning, approval, identity request, policy-checking, or notification logic from scratch. Input variables can alter behavior such as approval routing, provisioning mode, policy checking, notification behavior, target identity, requester, plan handling, and subprocess execution path. However, reuse requires discipline: the custom workflow must pass the correct variables, preserve expected types, and handle returned values correctly. Blindly calling an LCM subprocess without matching its contract can produce broken approvals or provisioning behavior. The proposed statement is therefore true because standard LCM subprocesses are intentionally reusable when controlled through documented workflow variables. References/topics: IdentityIQ Engineer - LCM workflows, subprocess reuse, workflow input variables, provisioning workflows, custom workflow development.
NEW QUESTION # 64
An organization is making a change at the regional level.
Many users of a financial system have incorrect entitlements. Some users are missing entitlements, and some users have excess entitlements. Work needs to be performed to clean up access.
Is this one of the IdentuylQ batch request types that can help meet this goal?
Solution: Delete Entitlement
- A. Yes
- B. No
Answer: B
Explanation:
The "Delete Entitlement" batch request type is not designed for cleaning up access by correcting or updating entitlements in bulk. Instead, "Delete Entitlement" is used to remove specific entitlements from the system entirely, which may not be what is needed if the goal is to correct incorrect entitlements (e.g., removing excess entitlements while adding missing ones). For the scenario described, where users need their entitlements corrected, other batch processes such as "Update Entitlement," "Revoke Access," or specific role re-assignment processes would be more appropriate.
Reference:
SailPoint IdentityIQ Batch Request Types Documentation
SailPoint IdentityIQ Administration Guide (Entitlement Management Sections)
NEW QUESTION # 65
Is this statement valid regarding the control and usability of the Debug pages in IdentitylQ?
Solution: The application server must be restarted after reloading the logging file through the Debug-Logging page.
- A. Yes
- B. No
Answer: B
Explanation:
The statement that the application server must be restarted after reloading the logging file through the Debug-Logging page is incorrect. SailPoint IdentityIQ allows you to reload the logging configuration from the Debug-Logging page without restarting the application server. The Debug-Logging page provides a way to dynamically reload the logging settings, including those in the log4j file, so that changes can take effect immediately without the need for a server restart.
Therefore, the correct answer is B. No.
Reference:
This conclusion is supported by the SailPoint IdentityIQ Administration Guide, which details how to use the Debug-Logging page to manage logging settings dynamically without requiring a server restart.
NEW QUESTION # 66
Can a Workgroup be used for the following scenario?
Solution: Automatically creating multiple groups based on the values of a single identity attribute.
- A. Yes
- B. No
Answer: B
Explanation:
A Workgroup in SailPoint IdentityIQ is a collection of users or identities grouped together for the purpose of task assignment, workflow approvals, or certifications. Workgroups are not typically used for automatically creating multiple groups based on the values of a single identity attribute. To achieve automatic grouping based on identity attributes, you would need to use dynamic roles or possibly rule-based population. These methods allow for creating roles or groups dynamically by evaluating identity attributes and assigning memberships accordingly.
Reference:
SailPoint IdentityIQ Administration Guide (Sections on Workgroups and Dynamic Roles) SailPoint IdentityIQ Configuration Guide (Role Management)
NEW QUESTION # 67
Can a Workgroup be used for the following scenario?
Solution: Providing a group of users with specific capabilities.
- A. Yes
- B. No
Answer: A
Explanation:
In SailPoint IdentityIQ, a Workgroup can indeed be used to provide a group of users with specific capabilities. Workgroups are collections of users that can be assigned roles, tasks, and permissions. By associating capabilities with a Workgroup, all members of that Workgroup will inherit the capabilities defined.
This feature is commonly used to manage teams or departments that need to share specific privileges, such as the ability to approve access requests or manage certifications. Configuring capabilities for a Workgroup is a standard practice within IdentityIQ to simplify permission management and ensure consistent access control across the group.
Therefore, the correct answer is A. Yes.
Reference:
This conclusion is drawn from the SailPoint IdentityIQ Administration Guide, which details how Workgroups function and how they can be used to assign capabilities and manage access control within the platform.
NEW QUESTION # 68
Is the following statement true about out-of-the-box reporting?
Solution: In the Reporting user interface, instances of reports are located on the 'My Reports' tab, and templates are located on the 'Reports' tab.
- A. Yes
- B. No
Answer: A
Explanation:
The statement is true. In the SailPoint IdentityIQ Reporting user interface, report templates are located on the "Reports" tab. These templates define the structure and parameters of reports but do not contain actual report data. Instances of reports, which are the actual generated reports containing data based on the templates, are located on the "My Reports" tab. The "My Reports" tab is used for viewing and managing reports that have been generated for a specific user.
Reference:
SailPoint IdentityIQ Reporting Guide
SailPoint IdentityIQ Administration Guide (Section on Reporting Interface)
NEW QUESTION # 69
An IdentitylQ engineer needs to extend attributes in an IdentitylQ database after the database has been created.
What are the four minimum steps necessary to achieve this goal?
Drag four options from the left into the answer area on the right, and place them in the correct order.
Answer:
Explanation:
NEW QUESTION # 70
Is this statement true about the Application, Identity, ManageAttribute, Bundle, and Link objects in IdentitylQ?
Solution: An Application object is not required to aggregate external user account information into IdentitylQ.
- A. Yes
- B. No
Answer: B
Explanation:
The statement that "An Application object is not required to aggregate external user account information into IdentityIQ" is false. In SailPoint IdentityIQ, an Application object is essential for aggregating (importing) external user account information. The Application object defines the connection settings, schema, and mapping that enable IdentityIQ to connect to external systems and retrieve identity data. Without an Application object, IdentityIQ would not have the necessary configuration to establish a connection and aggregate user data from external sources.
Reference:
SailPoint IdentityIQ Administration Guide (Section on Applications and Aggregation) SailPoint IdentityIQ Integration and Configuration Guide
NEW QUESTION # 71
Is this what should be performed in order to generate the database script to extend Application attributes in the IdentitylQ database on the initial installation?
Solution: Run a build with the updated schema placed inside it.
- A. Yes
- B. No
Answer: B
Explanation:
Running a build with the updated schema placed inside it is not the correct procedure to generate the database script to extend Application attributes in the IdentityIQ database during the initial installation. To extend the schema, you typically need to define the changes in a specific XML schema file and then generate the corresponding database scripts using IdentityIQ tools designed for schema extension. A build process does not inherently generate the required database scripts for extending attributes.
Reference:
SailPoint IdentityIQ Schema Configuration Guide
SailPoint IdentityIQ Installation and Setup Guide
NEW QUESTION # 72
A client needs a custom quicklink, which only managers can launch, in order to launch a simple workflow.
Is this a valid step to take during the development of this custom quicklink?
Proposed Solution:
Place a quicklink object on the workflow that is to be launched.
- A. Yes
- B. No
Answer: B
Explanation:
This is not a valid development step. A Quicklink is configured as an IdentityIQ object that exposes an action to users through the UI and can be configured to launch a workflow. The workflow does not contain or "host" the Quicklink object. The relationship is the other way around: the Quicklink references the workflow it should launch. To restrict the Quicklink to managers only, the engineer should configure visibility, population, capability, or dynamic eligibility logic so only manager identities can see or execute it. Then the Quicklink configuration should identify the workflow to invoke and pass any required arguments into that workflow. Placing a Quicklink object "on" the workflow is not how IdentityIQ Quicklink architecture works.
The proposed solution confuses the launching object with the launched process. References/topics: IdentityIQ Engineer - Quicklink object, workflow launch configuration, manager-only visibility, population rules, workflow arguments.
NEW QUESTION # 73
Is this statement true about certifications?
Solution: All certifications include generation, the active period, sign-off, and the end period.
- A. Yes
- B. No
Answer: A
Explanation:
The statement that " All certifications include generation, the active period, sign-off, and the end period " is true. These stages are fundamental to the certification process in SailPoint IdentityIQ:
* Generation: This is the initial stage where the certification campaign is created. During this phase, the system generates the list of items (such as access, roles, or entitlements) that need to be reviewed.
* Active Period: Once the certification is generated, it enters the active period. During this time, the designated reviewers are responsible for examining the items in the certification, making decisions (such as approving or revoking access), and providing any necessary comments.
* Sign-off: After the active period, the certification moves into the sign-off stage. Here, the final approver (s) review the decisions made during the active period and formally approve or reject the certification outcomes.
* End Period: Finally, the end period marks the conclusion of the certification campaign. The certification is closed, and the results are archived. Any necessary actions, such as revoking access or triggering workflows based on the certification decisions, are implemented.
These stages are essential to the structured process that ensures all access rights are properly reviewed and either maintained or adjusted according to the organization ' s policies.
SailPoint IdentityIQ Certification Administrator ' s Guide
SailPoint IdentityIQ Certification Process Documentation
SailPoint IdentityIQ Administration Guide (Sections on Certification Lifecycle and Workflow)
NEW QUESTION # 74
Match the following IdentitylQ console commands To their functions.
Use the drop-down menus to select your answers. Answer options from the drop-down menus may only be used once Some will not be used at all.
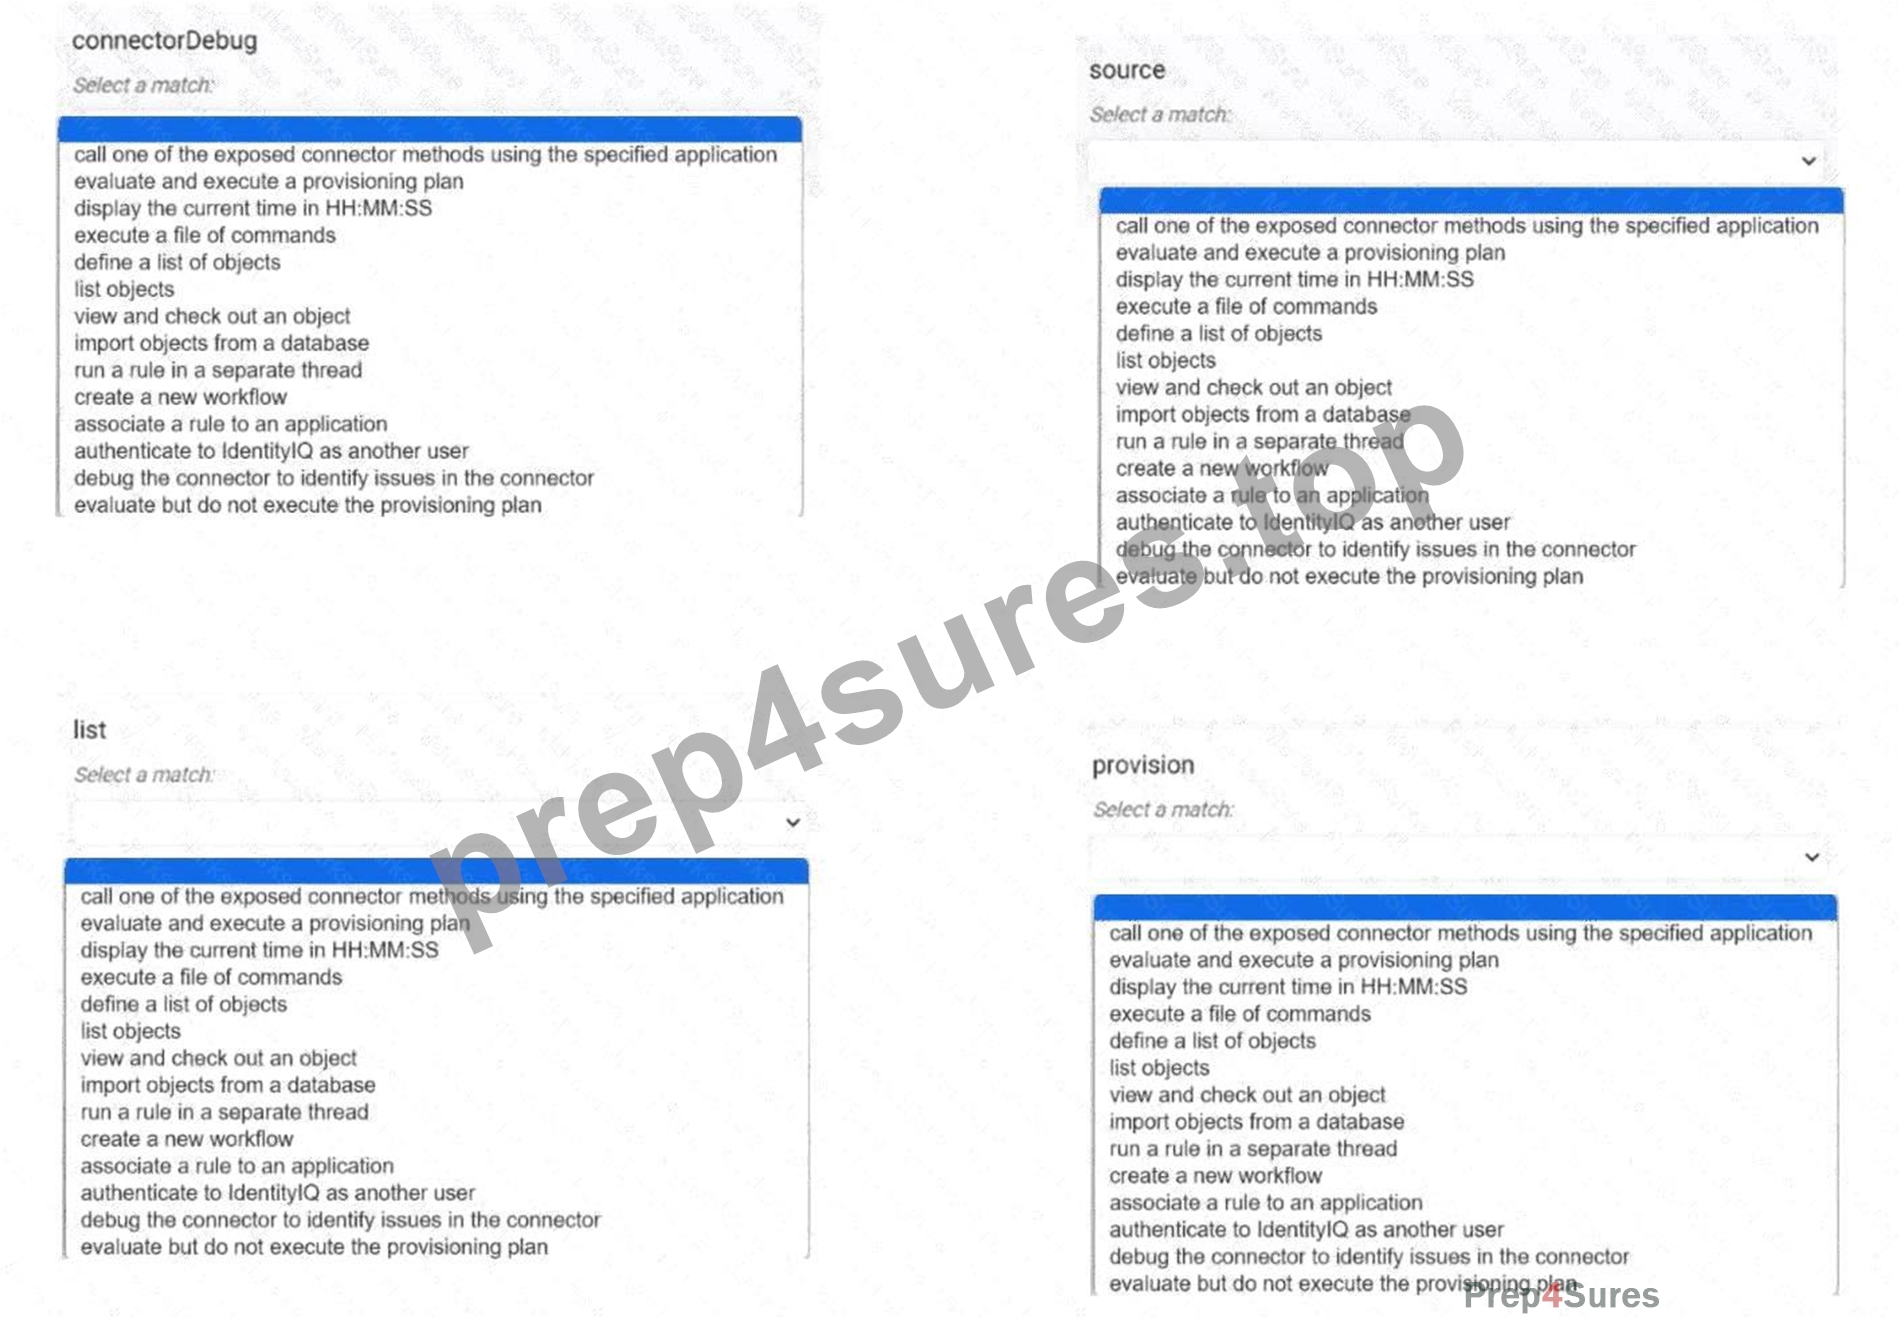
Answer:
Explanation:
Explanation:
Here's how the SailPoint IdentityIQ console commands correspond to their respective functions:
* connectorDebug: debug the connector to identify issues in the connector.
* source: authenticate to IdentityIQ as another user.
* list: list objects.
* provision: evaluate and execute a provisioning plan.
Comprehensive Detailed Explanation with All IdentityIQ Engineer References
* connectorDebug:
SailPoint IdentityIQ Console Guide (section on connector troubleshooting).
source:
This command allows you to authenticate as another user within the IdentityIQ system. It ' s useful for testing user-specific actions or behaviors without logging out and back in.Reference: SailPoint IdentityIQ Admin Guide (section on user authentication and delegation).
list:
This function returns a list of objects or entities within the system. In IdentityIQ, objects could include applications, roles, policies, and more.Reference: SailPoint IdentityIQ Console Reference Guide (list and query commands).
provision:
The provision command evaluates and executes a provisioning plan. This is the actual process that implements changes in user access across connected systems based on the identity lifecycle event.Reference:
SailPoint IdentityIQ Provisioning Guide (execution of provisioning plans).
By matching these commands to their respective functions, the detailed functionalities of IdentityIQ's console tools are properly understood for administrative and troubleshooting purposes.
NEW QUESTION # 75
An engineer needs to first create a custom audit event and then set up an associated report. What are four steps to accomplish this goal?
Solution: Create and load a Custom Audit Report TaskDefinition XML and corresponding Custom Audit Report Form XML.
- A. Yes
- B. No
Answer: A
Explanation:
Creating and loading a Custom Audit Report TaskDefinition XML and corresponding Custom Audit Report Form XML is indeed part of the process for setting up a custom audit report in SailPoint IdentityIQ. The TaskDefinition XML defines the report task, and the Form XML defines the user interface for running the report. These steps are essential to creating a custom audit report, and the solution correctly outlines a valid approach. Refer to the SailPoint IdentityIQ Reporting Guide, particularly the section on creating custom reports and forms, for more detailed instructions.
NEW QUESTION # 76
Is this a purpose of an IdentityIQ certification?
Proposed Solution:
to ensure SailPoint is in compliance with the ISO 9001 government regulation
- A. Yes
- B. No
Answer: B
Explanation:
No. IdentityIQ certifications are used to review and attest access, roles, entitlements, account group memberships, policy violations, or other governance items. They are not designed to ensure "SailPoint" itself is compliant with ISO 9001, and ISO 9001 is not a government regulation in the way the proposed solution states. ISO 9001 is a quality management standard, not an access-governance regulation that IdentityIQ certifications directly enforce. An organization may use IdentityIQ certification evidence as part of broader compliance programs, but the certification's direct purpose is access review: confirming that users have appropriate access and that inappropriate access is revoked, remediated, or justified. The wording is wrong both in target and scope. The certification process supports customer governance/compliance objectives, not SailPoint corporate ISO compliance. References/topics: IdentityIQ Engineer - certification purpose, access review, compliance evidence, entitlement review, role review, governance controls.
NEW QUESTION # 77
An IdentitylQ engineer needs to extend attributes in an IdentitylQ database after the database has been created.
What are the four minimum steps necessary to achieve this goal?
Drag four options from the left into the answer area on the right, and place them in the correct order.
Answer:
Explanation:
Explanation:
The four minimum steps necessary to extend attributes in an IdentityIQ database after it has been created, in the correct order, are:
* Update the corresponding hibernate file with the new attributes.
* The Hibernate mapping file needs to be updated with the new attributes so that the SailPoint IdentityIQ application is aware of the new columns or properties in the database. This step ensures that the object-relational mapping (ORM) reflects the updated data model.
* Run the command to generate the script to update the IdentityIQ database.
* After updating the Hibernate file, a schema update script is generated. This script contains the necessary SQL commands to modify the database schema based on the new attributes added in the Hibernate file.
* Shut down the application server and then run the generated extendedSchema script on the IdentityIQ database.
* Before applying schema changes, the application server must be stopped to avoid any transactional conflicts. Afterward, the extendedSchema script is run on the database to apply the new attributes.
* Start the application server and update the corresponding ObjectConfig.
* Once the database schema is updated, restart the IdentityIQ application server and modify the ObjectConfig in SailPoint to register the new attributes for use within the IdentityIQ platform.
Comprehensive Detailed Explanation with All IdentityIQ Engineer References
* Updating the Hibernate File: This step involves modifying the Hibernate XML or annotation-based mapping files to reflect the new attributes that are being added to the database. SailPoint IdentityIQ uses Hibernate as its ORM, and any new database fields must first be defined at this layer.
* Generating the Schema Update Script: SailPoint provides a command (usually via iiq console or build tools) that reads the updated Hibernate mapping and generates a database-specific script to alter the schema. This ensures that the database is modified in a way that matches the application ' s expectations.
* Running the Schema Update Script: With the application server stopped, the schema update script is executed on the database. This step adds the new columns, indexes, or constraints that are required for the extended attributes.
* Updating the ObjectConfig: Once the database is updated and the application server is running again, the ObjectConfig (typically located in the IdentityIQ admin UI) must be updated to incorporate the new fields. This step ensures that these new attributes are accessible to workflows, forms, and identity data within the system.
SailPoint IdentityIQ Installation and Configuration Guide (sections on extending the data model and schema updates).
NEW QUESTION # 78
Is the following statement true?
Proposed Solution:
A Bundle profile must be associated to an Identity object.
- A. Yes
- B. No
Answer: B
Explanation:
No. A Bundle represents a role in IdentityIQ, and a Bundle profile is part of role definition logic, not something that must be associated directly to an Identity object. Profiles are used to describe conditions, constraints, or entitlement/application criteria associated with a role. Identities may be assigned roles, detected as matching roles, or evaluated against role profiles, but the Bundle profile itself is not required to be associated to a specific Identity object. This distinction is important because IdentityIQ's role model is object- based: roles exist independently from the identities that hold them. A profile defines what the role means or how it is detected; identity role membership is a separate relationship. Saying that a Bundle profile must be associated with an Identity object incorrectly collapses role definition and identity assignment into one concept. References/topics: IdentityIQ Engineer - Bundle object, role profiles, role detection, role assignment, Identity object relationships.
NEW QUESTION # 79
Is this an example of a mover lifecycle event?
Solution: An employee quits their job and needs all of their accounts disabled.
- A. Yes
- B. No
Answer: B
Explanation:
This scenario describes an employee quitting their job and needing all of their accounts disabled, which aligns with a leaver lifecycle event rather than a mover event. A leaver event typically involves the deactivation of accounts and removal of access for users who are leaving the organization entirely, whereas a mover event involves changes to roles or access as part of an internal transition (e.g., promotion, transfer).
Therefore, the correct answer is B. No.
NEW QUESTION # 80
The JVM Memory page on IdentitylQ displays the following information:
Solution: How much memory is currently allocated to the JVM heap?
Type your numerical response into the box below.
Answer:
Explanation:
725.617 MB
Explanation:
The " Total Memory " value displayed on the JVM Memory page indicates the amount of memory currently allocated to the JVM heap. In the image provided, the " Total Memory " is shown as 725.617 MB. This is the amount of memory that the JVM heap is currently using, meaning it has been allocated and is available for the JVM to use.
SailPoint IdentityIQ Performance Tuning and Monitoring Guide
SailPoint IdentityIQ Administration Guide (JVM and Memory Management Sections)
NEW QUESTION # 81
Can this be achieved using Rapid Setup user interface configuration options?
Solution: Disable an account and remove all its entitlements on a particular application during Leaver events.
- A. Yes
- B. No
Answer: A
Explanation:
The Rapid Setup user interface configuration options in IdentityIQ can be used to disable an account and remove all its entitlements on a particular application during Leaver events. Rapid Setup is designed to simplify the configuration of common identity lifecycle processes, including handling leaver (termination) events. When configuring these events, you can specify actions such as disabling accounts and removing entitlements from specific applications as part of the termination process.
Reference:
SailPoint IdentityIQ Rapid Setup Guide
SailPoint IdentityIQ Lifecycle Manager Guide (Sections on Lifecycle Event Configuration)
NEW QUESTION # 82
Can this be achieved using Rapid Setup user interface configuration options?
Solution: Reassign all object ownership to the user's manager during Leaver and Termination events.
- A. Yes
- B. No
Answer: B
Explanation:
Reassigning all object ownership to a user's manager during Leaver and Termination events is a complex process that typically involves custom logic or workflows to ensure that all owned objects (like access, certifications, roles, etc.) are correctly reassigned.
The Rapid Setup interface is primarily designed for standard lifecycle management tasks, such as role assignments, account enabling/disabling, and certifications. It does not inherently support the automatic reassignment of object ownership based on lifecycle events such as Leaver and Termination events.
This kind of reassignment would typically require a custom rule or workflow to track and reassign all owned objects, which falls outside the scope of what Rapid Setup can handle directly. Therefore, the correct answer is B. No.
Reference:
This information is supported by the SailPoint IdentityIQ Lifecycle Manager Guide, which outlines what is possible through Rapid Setup and what would require custom development.
NEW QUESTION # 83
......
Dumps Real SailPoint IdentityIQ-Engineer Exam Questions [Updated 2026]: https://www.prep4sures.top/IdentityIQ-Engineer-exam-dumps-torrent.html
Prepare IdentityIQ-Engineer Question Answers Free Update With 100% Exam Passing Guarantee [2026]: https://drive.google.com/open?id=1FrcUoQ5gf5sbg8Wd1jvwNRattfq77--5