


(Feb-2024) Latest CS0-002 Dumps for Success in Actual CompTIA Certified
Changing the Concept of CS0-002 Exam Preparation 2024
CompTIA Cybersecurity Analyst (CySA+) certification exam or CS0-002, is an advanced-level certification that validates the skills and knowledge of IT professionals in the field of cybersecurity. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification exam is designed to assess the skills required to identify, prevent, and respond to cybersecurity threats and vulnerabilities. CS0-002 exam covers a wide range of topics, including threat and vulnerability management, incident response, security architecture and toolsets, and compliance and regulations.
NEW QUESTION # 140
A security analyst observes a large amount of scanning activity coming from an IP address outside the organization's environment. Which of the following should the analyst do to block this activity?
- A. Create an IPS rule to block the subnet.
- B. Create a firewall rule to block the IP address.
- C. Sinkhole the IP address.
- D. Close all unnecessary open ports.
Answer: C
NEW QUESTION # 141
An analyst is performing penetration testing and vulnerability assessment activities against a new vehicle automation platform.
Which of the following is MOST likely an attack vector that is being utilized as part of the testing and assessment?
- A. FaaS
- B. CAN bus
- C. GPS
- D. SoC
- E. RTOS
Answer: E
Explanation:
Explanation
IoT devices also often run real-time operating systems (RTOS). These are either special purpose operating systems or variants of standard operating systems designed to process data rapidly as it arrives from sensors or other IoT components.
NEW QUESTION # 142
The software development team pushed a new web application into production for the accounting department. Shortly after the application was published, the head of the accounting department informed IT operations that the application was not performing as intended. Which of the following SDLC best practices was missed?
- A. User acceptance testing
- B. Fuzzing
- C. Peer code reviews
- D. Static code analysis
- E. Regression testing
Answer: A
NEW QUESTION # 143
A security engineer is reviewing security products that identify malicious actions by users as part of a company's insider threat program. Which of the following is the MOST appropriate product category for this purpose?
- A. UEBA
- B. SOAR
- C. WAF
- D. SCAP
Answer: A
Explanation:
UEBA stands for User and Entity Behavior Analytics and was previously known as user behavior analytics (UBA).
NEW QUESTION # 144
A security analyst is looking at the headers of a few emails that appear to be targeting all users at an organization:

Which of the following technologies would MOST likely be used to prevent this phishing attempt?
- A. DMARC
- B. S/IMAP
- C. STP
- D. DNSSEC
Answer: A
NEW QUESTION # 145
During a routine log review, a security analyst has found the following commands that cannot be identified from the Bash history log on the root user.
Which of the following commands should the analyst investigate FIRST?
- A. Line 5
- B. Line 3
- C. Line 1
- D. Line 6
- E. Line 4
- F. Line 2
Answer: F
NEW QUESTION # 146
A proposed network architecture requires systems to be separated from each other logically based on defined risk levels. Which of the following explains the reason why an architect would set up the network this way?
- A. To reduce the attack surface of those systems by segmenting the network based on risk
- B. To complicate the network and frustrate a potential malicious attacker
- C. To create a design that simplifies the supporting network
- D. To reduce the number of IP addresses that are used on the network
Answer: A
NEW QUESTION # 147
When investigating a compromised system, a security analyst finds the following script in the /tmp directory:
Which of the following attacks is this script attempting, and how can it be mitigated?
- A. This is a password-dictionary attack, and it can be mitigated by forcing password changes every 30 days.
- B. This is a credential-stuffing attack, and it can be mitigated by using multistep authentication.
- C. This is a password-hijacking attack, and it can be mitigated by using strong encryption protocols.
- D. This is a password-spraying attack, and it can be mitigated by using multifactor authentication.
Answer: D
Explanation:
https://owasp.org/www-community/attacks/Password_Spraying_Attack
A credential stuffing attack would be using the full credentials and most likely being used across many common platforms. A credential stuffing attack depends on the reuse of passwords. With so many people reusing their passwords for multiple accounts, just one set of credentials is enough to expose most or all of their accounts.
NEW QUESTION # 148
A security analyst is reviewing a new Internet portal that will be used for corporate employees to obtain their pay statements. Corporate policy classifies pay statement information as confidential, and it must be protected by MFA. Which of the following would best fulfill the MFA requirement while keeping the portal accessible from the internet?
- A. Moving the internet portal server to a DMZ that is only accessible from the corporate VPN and requiring a username and password
- B. Distributing a shared password that must be provided before the internet portal loads and requiring a username and password
- C. Requiring the internet portal to be accessible from only the corporate SSO internet endpoint and requiring a smart card and PIN
- D. Obtaining home public IP addresses of corporate employees to implement source IP restrictions and requiring a username and password
Answer: C
Explanation:
Requiring the internet portal to be accessible from only the corporate SSO internet endpoint and requiring a smart card and PIN. This option provides the best MFA requirement because it uses two factors of authentication: something you have (smart card) and something you know (PIN). It also restricts access to the portal from a trusted source (corporate SSO internet endpoint).
NEW QUESTION # 149
A security analyst, who is working for a company that utilizes Linux servers, receives the following results from a vulnerability scan: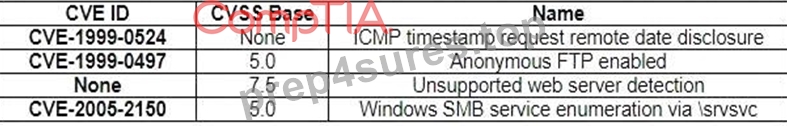
Which of the following is MOST likely a false positive?
- A. Windows SMB service enumeration via \srvsvc
- B. Unsupported web server detection
- C. ICMP timestamp request remote date disclosure
- D. Anonymous FTP enabled
Answer: A
NEW QUESTION # 150
An analyst wants to identify hosts that are connecting to the external FTP servers and what, if any, passwords are being used. Which of the following commands should the analyst use?
- A. ftp ftp.server -p 21
- B. tcpdump -X dst port 21
- C. telnet ftp.server 21
- D. nmap -o ftp.server -p 21
Answer: B
NEW QUESTION # 151
A security analyst found an old version of OpenSSH running on a DMZ server and determined the following piece of code could have led to a command execution through an integer overflow;
Which of the following controls must be in place to prevent this vulnerability?
- A. Sanitize user inputs, avoiding small numbers that cannot be handled in the memory.
- B. Use built-in functions from libraries to check and handle long numbers properly.
- C. Convert all integer numbers in strings to handle the memory buffer correctly.
- D. Implement float numbers instead of integers to prevent integer overflows.
Answer: B
NEW QUESTION # 152
A security analyst is researching ways to improve the security of a company's email system to mitigate emails that are impersonating company executives. Which of the following would be BEST for the analyst to configure to achieve this objective?
- A. A sandbox to check incoming mad
- B. A TXT record on the name server for SPF
- C. DNSSEC keys to secure replication
- D. Domain Keys identified Man
Answer: D
Explanation:
Domain Keys Identified Mail (DKIM) is an email authentication method that uses a digital signature to let the receiver of an email know that the message was sent and authorized by the owner of a domain1 DKIM helps prevent phishing emails that spoof or impersonate other domains by verifying the identity and integrity of the sender. DKIM works by adding a DKIM signature header to each outgoing email message, which contains a hash value of selected parts of the message and the domain name of the sender. The sender's domain also publishes a public key in its DNS records, which can be used by the receiver to decrypt the DKIM signature and compare it with its own hash value of the message. If they match, it means that the message was not altered in transit and that it came from the claimed domain.
NEW QUESTION # 153
A cybersecurity analyst needs to determine whether a large file named access log from a web server contains the following loC:
../../../../bin/bash
Which of the following commands can be used to determine if the string is present in the log?
- A. grep "../../../../bin/bash" 1 cat access.log
- B. grep "../../../. ./bin/bash" < access.log
- C. cat access.log > grep "../../../ ../bin/bash"
- D. echo access.log | grep "../../../../bin/bash"
Answer: B
NEW QUESTION # 154
During a routine review of service restarts a security analyst observes the following in a server log:
Which of the following is the GREATEST security concern?
- A. The process identifiers for the running service change
- B. The PIDs are continuously changing
- C. Four consecutive days of monitoring are skipped in the tog
- D. The daemon's binary was AChanged
Answer: D
NEW QUESTION # 155
A security analyst is investigating a malware infection that occurred on a Windows system. The system was not connected to a network and had no wireless capability Company policy prohibits using portable media or mobile storage The security analyst is trying to determine which user caused the malware to get onto the system Which of the following registry keys would MOST likely have this information?
A)
B)
C)
D)
- A. Option C
- B. Option D
- C. Option B
- D. Option A
Answer: A
NEW QUESTION # 156
Because some clients have reported unauthorized activity on their accounts, a security analyst is reviewing network packet captures from the company's API server. A portion of a capture file is shown below:
POST /services/v1_0/Public/Members.svc/soap <s:Envelope+xmlns:s="http:// schemas.s/soap/envelope/"><s:Body><GetIPLocation+xmlns="http://tempuri.org/">
<request+xmlns:a="http://schemas.somesite.org"+xmlns:i="http://www.w3.org/2001/ XMLSchema-instance"></s:Body></s:Envelope> 192.168.1.22 - - api.somesite.com 200
0 1006 1001 0 192.168.1.22
POST /services/v1_0/Public/Members.svc/soap <<a:Password>Password123</
a:Password><a:ResetPasswordToken+i:nil="true"/>
<a:ShouldImpersonatedAuthenticationBePopulated+i:nil="true"/
><a:Username>[email protected]</a:Username></request></Login></s:Body></ s:Envelope> 192.168.5.66 - - api.somesite.com 200 0 11558 1712 2024 192.168.4.89 POST /services/v1_0/Public/Members.svc/soap <s:Envelope+xmlns:s="http:// schemas.xmlsoap.org/soap/envelope/"><s:Body><GetIPLocation+xmlns="http:// tempuri.org/"> <a:IPAddress>516.7.446.605</a:IPAddress><a:ZipCode+i:nil="true"/
></request></GetIPLocation></s:Body></s:Envelope> 192.168.1.22 - -
api.somesite.com 200 0 1003 1011 307 192.168.1.22
POST /services/v1_0/Public/Members.svc/soap <s:Envelope+xmlns:s="http:// schemas.xmlsoap.org/soap/envelope/"><s:Body><IsLoggedIn+xmlns="http:// tempuri.org/"> <request+xmlns:a="http://schemas.datacontract.org/2004/07/ somesite.web+xmlns:i="http://www.w3.org/2001/XMLSchema- instance"><a:Authentication>
<a:ApiToken>kmL4krg2CwwWBan5BReGv5Djb7syxXTNKcWFuSjd</
a:ApiToken><a:ImpersonateUserId>0</a:ImpersonateUserId><a:LocationId>161222</ a:LocationId> <a:NetworkId>4</a:NetworkId><a:ProviderId>''1=1</ a:ProviderId><a:UserId>13026046</a:UserId></a:Authentication></request></ IsLoggedIn></s:Body></s:Envelope> 192.168.5.66 - - api.somesite.com 200 0 1378
1209 48 192.168.4.89
Which of the following MOST likely explains how the clients' accounts were compromised?
- A. An XSS scripting attack was carried out on the server.
- B. The clients' authentication tokens were impersonated and replayed.
- C. The clients' usernames and passwords were transmitted in cleartext.
- D. A SQL injection attack was carried out on the server.
Answer: B
NEW QUESTION # 157
......
Study Guides
- CompTIA Cybersecurity Analyst (CySA+) CS0-002 Certification Guide 2nd EditionHere's another top-rated study material that’ll help you master the topics relevant to your CySA+ certification exam. It features end-of-chapter questions to assist you in reviewing lessons and reinforcing knowledge, preparation tasks to guide you in learning the key concepts, and mock questions. The purchase package also includes access to online training software and flashcards. The guide is written by Troy McMillan, a leading IT certification instructor.
- CompTIA CySA+ CS0-002 Certification Study Guide by James PengellyThis is the official study guide for CS0-002 exam. It was created by CompTIA and was thoroughly evaluated to ensure that it teaches the skills that position students for success in the certification exam. Beginning with the fundamentals, it covers all you need to know to master the objectives. The book is structured for easy, self-paced study. A sample is available on the CompTIA site for free download.
- CompTIA CySA+ Cybersecurity Analyst Certification Passport (Exam CS0-002)This portable, low-cost tool is your fast-track route to becoming CompTIA CySA+ certified in record time. The Author, Bobby E. Rogers, gets to the essence of what you need to know to pass the exam. This obstinate focus helps ensure that every page puts you closer to your goal: to obtain your CySA+ certification.
- CompTIA CySA+ Study Guide CS0-002 (2nd Edition)Authored by leading security experts Mike Chapple and Dave Seidl, this is another book that's sure to make you ready for the test. It is a comprehensive resource that covers 100% of the revised CS0-002 exam objectives, offering concise information on important security topics. Purchasing this book also provides you with instant one-year access to useful online study tools. These include a test bank containing two practice exams to help gauge your readiness and boost your confidence, 100 electronic flashcards to help reinforce learning, and a glossary, giving you quick access to key terms.
CS0-002 Exam Crack Test Engine Dumps Training With 371 Questions: https://www.prep4sures.top/CS0-002-exam-dumps-torrent.html
Getting CS0-002 Certification Made Easy: https://drive.google.com/open?id=1djGefw9eHVANFOa4et_Tx9A2lAnqunf3